Board Member & Advisory
Security & Infrastructure Leader | Board Member | Advisor | Risk & Governance Expert
Kris Boike is a seasoned security and infrastructure leader, board member, and risk strategist who brings governance perspective, regulatory credibility, and business-aligned risk judgment to boards, executive teams, and audit and risk committees.
How Kris Helps:
Risk Appetite Alignment
Enterprise and Technology Risk Integration
Connecting technology risk programs to enterprise risk management so leadership sees one clear, cohesive picture of exposure and readiness.
Regulatory and Compliance Judgment
Governance and Oversight Perspective
Security Transformation Discipline
Threat and Vulnerability Readiness
Governance & Board-Level Value
Areas of Advisory
Cybersecurity Strategy & Risk Decisioning
Technology & Infrastructure Oversight
Regulatory, Compliance & GRC
Enterprise Risk & Third-Party Risk
Executive & Board Alignment
Strengthening how security leaders brief boards, measure performance, and translate technical risk into decisions leadership can act on.
“Boards should not just oversee security, they should govern it: setting risk appetite, demanding accountability, and turning complex technology risk into direction the whole organization can act on.”
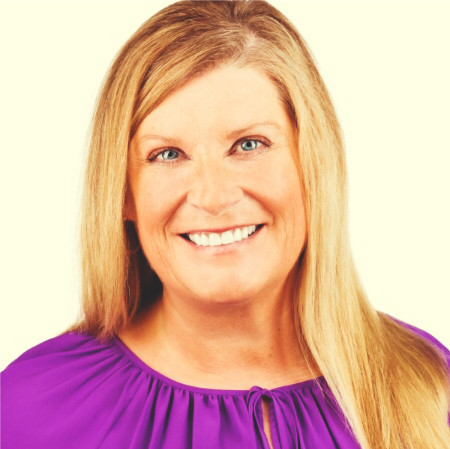
Kris Boike
Head of Information Security at Dorsey & Whitney